Modeling AI agents: new classes and Threat Patterns
New modules for AI agents and their tools, and an analysis that finds threats spanning several elements of a model.
dether.net
Dethernety can now model AI agents and the systems around them. We have added a vendor-neutral class library and a new analysis called Threat Patterns.
Classes for agentic systems
Five modules add 50 classes. They cover agents and their runtimes, MCP servers and gateways, hosted and self-hosted models, vector stores and memory, self-hosted platforms such as n8n and Dify, and controls such as human approval and tool authorization. Separate AWS and Azure modules cover services including Bedrock AgentCore, Foundry agents, Copilot Studio and Microsoft 365 Copilot.
MITRE ATT&CK has no technique for prompt injection or tool poisoning. MITRE ATLAS does, so ATLAS joined the platform's reference data in release 0.10.0, and the new classes cite it.
Threat Patterns
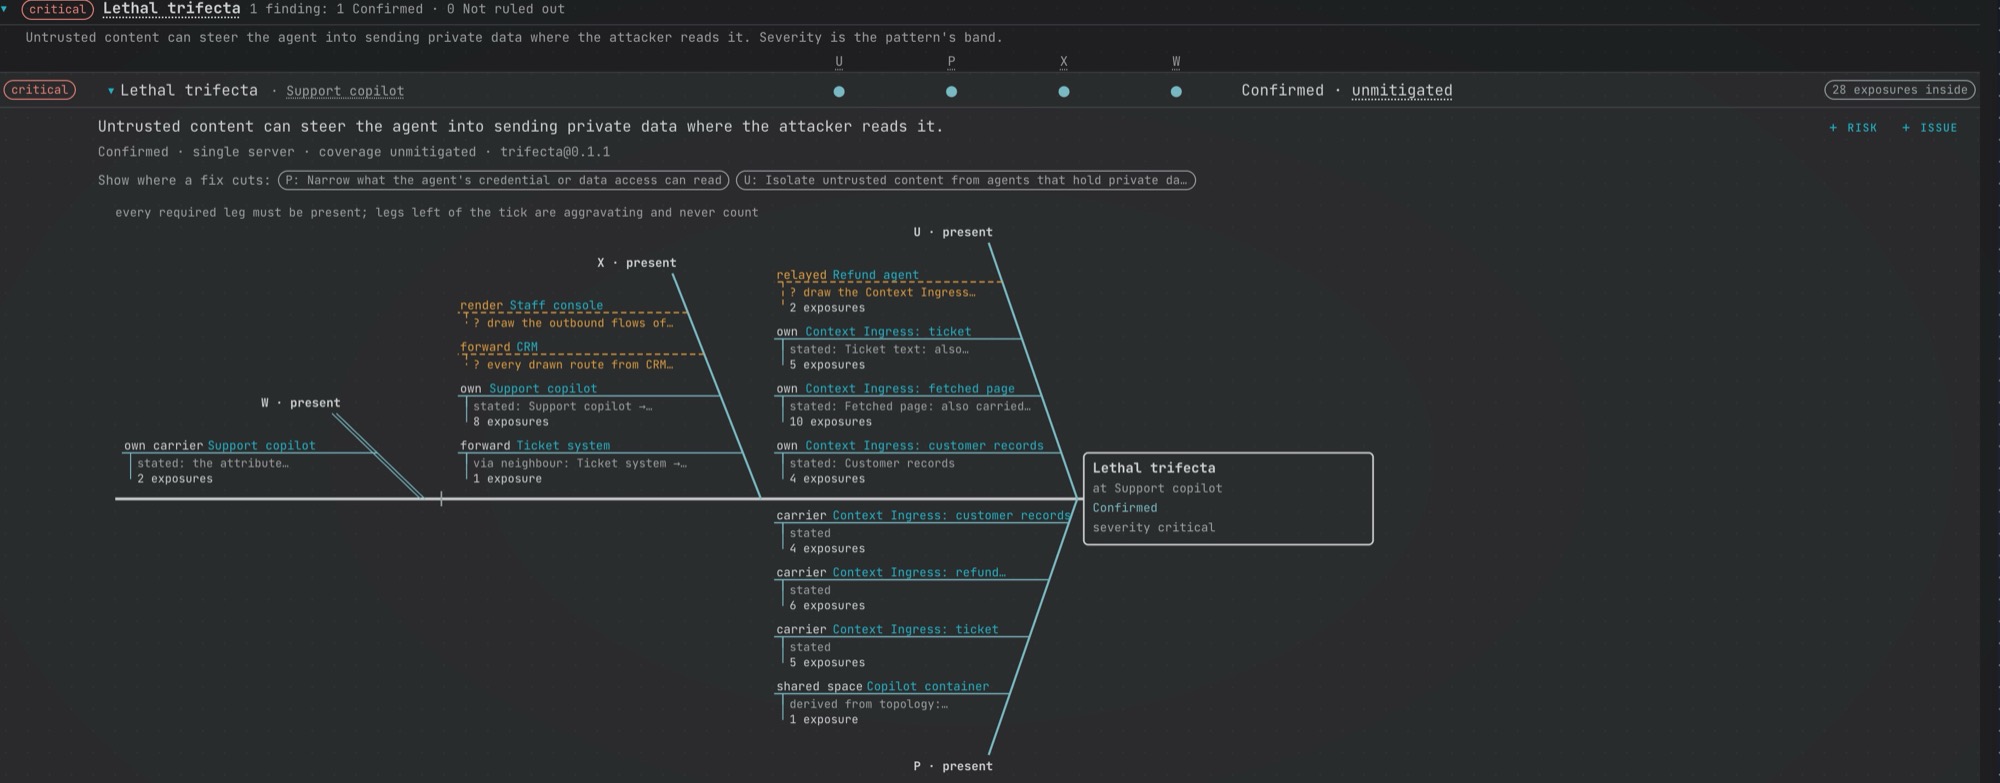
Some threats appear only when several elements line up. Take an agent that reads content anyone can write, can reach private data, and can send data where an outsider can read it. Simon Willison has called this combination the lethal trifecta.
Threat Patterns reads the whole model and looks for combinations like this one. Others include:
- Credential chain: a foothold in the agent stack reaches a credential that unlocks sensitive data or actions.
- Injection to action: untrusted content can trigger a write or code execution that nobody approves.
- Delegation hop: an agent exposed to untrusted content hands the work to an agent that holds the other conditions.
The analysis runs without AI. A finding has the pattern's fixed severity band but no risk score. It is confirmed in the model when every required condition is present. If the model does not say enough to decide, the finding reads Not ruled out, and the analysis names the fact it needs.
It reads the model, not the running system, so a confirmed finding describes the design and is not proof of an exploit.
The classes and the patterns will be sold as an Agentic AI package in BYODt, our subscription edition, which is in development. Read more about Threat Patterns.
dether.net
More articles
BYODt is available
BYODt (Bring Your Own Dethernety): host the platform yourself and get module packages served from our cloud. From EUR 25 per package per month.
November 4, 2026
Threat modeling agentic architectures: two new videos
A seven-minute video and a 90-second short on threat modeling AI agents, using a fictional support copilot.
October 16, 2026